

Cookie policy, consent snippets and recognizing visitors without cookies
On this page
Three things in Setup > Website > Monitoring decide what the monitoring script stores: the Cookie policy, the Recognise visitors without cookies switch, and two consent snippets your site calls with the visitor's answer.
How it works
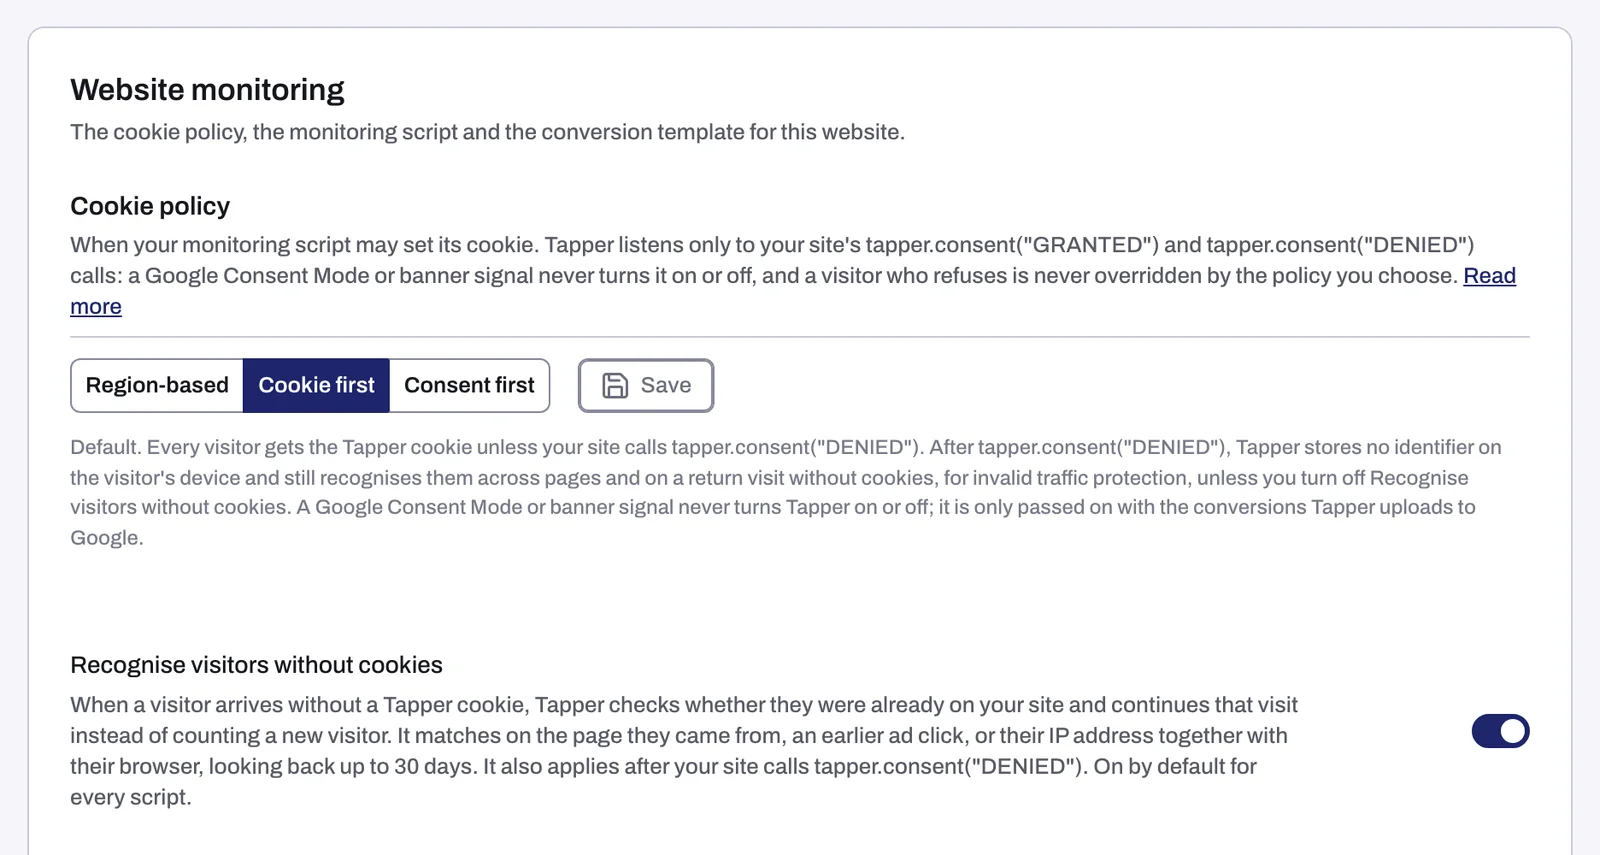
Tapper listens to exactly two calls from your site: window.tapper.consent("GRANTED") and window.tapper.consent("DENIED"). As the tab puts it, "a Google Consent Mode or banner signal never turns it on or off, and a visitor who refuses is never overridden by the policy you choose."
- The Cookie policy decides what happens before your site makes either call.
- A call from your site always wins over the policy, for that visitor.
- When Tapper may not set its cookie, it can still recognize a returning visitor for invalid traffic protection, unless you turn off Recognise visitors without cookies.
Google Consent Mode answers are used only for what Tapper hands to ad platforms: conversions Tapper uploads to Google carry the visitor's ad_user_data and ad_personalization answers.
The cookie policy
| Policy | What it does |
|---|---|
| Region-based | Visitors in the EEA and the UK get no Tapper cookie or identifier until your site calls tapper.consent("GRANTED"). Everyone else gets the cookie unless your site calls tapper.consent("DENIED"). |
| Cookie first | Every visitor gets the Tapper cookie unless your site calls tapper.consent("DENIED"). After that call, Tapper stores no identifier on the visitor's device. |
| Consent first | No visitor gets a Tapper cookie or identifier until your site calls tapper.consent("GRANTED"). |
When a visitor is refused with tapper.consent("DENIED"), the most Tapper keeps in their browser is a short note that they said no, so the next pages of that visit respect it. The note holds no identifier and goes when the tab is closed.
A new entity starts on Cookie first.
Change the policy
- With more than one protected entity, pick the entity in the switcher at the top of the sidebar.
- Under Setup, click Website, then Monitoring. Cookie policy is the first tab.
- Click Region-based, Cookie first or Consent first, and read the line underneath.
- Click Save. Nothing changes until you do.
The script uses the new policy from the next visit. Only workspace Owners and Admins can change it.
Recognizing visitors without cookies
The Recognise visitors without cookies switch sits under the cookie policy and is on by default. When a visitor arrives without a Tapper cookie, Tapper checks whether they were already on your site and continues that visit instead of counting a new one. It matches on the page they came from, an earlier ad click, or their IP address together with their browser, looking back up to 30 days. It also applies after tapper.consent("DENIED").
Turn it off only if you do not want Tapper to link visits without a cookie at all. Only Owners and Admins can change it.
The consent snippets
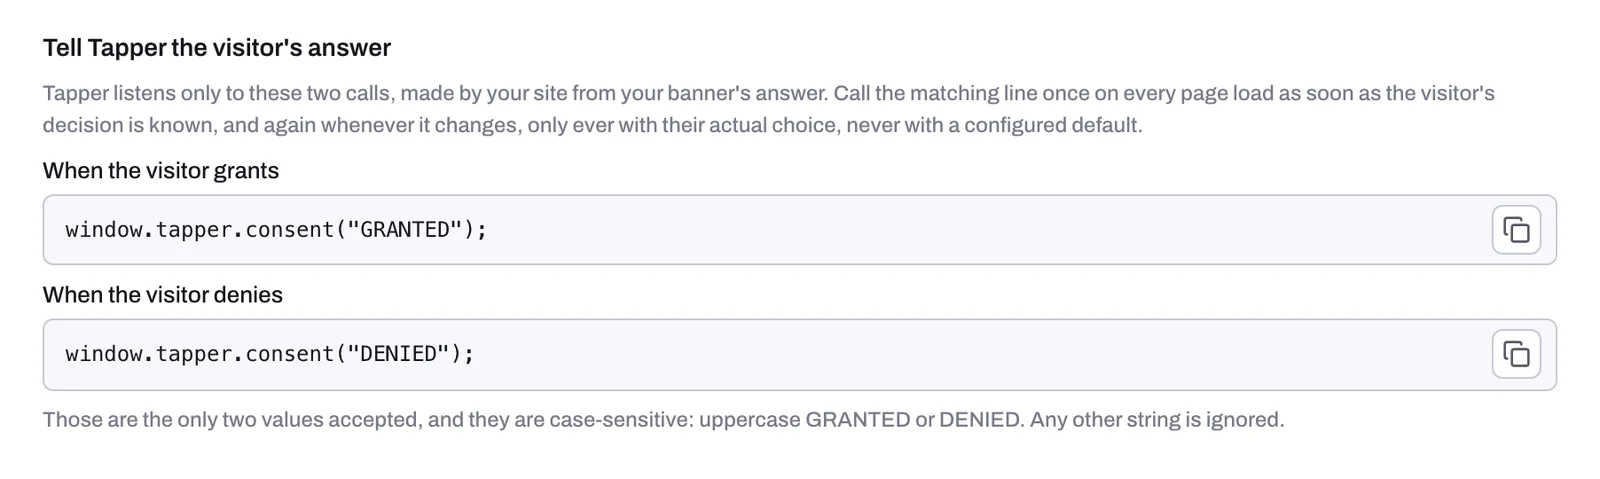
Below the monitoring script, Tell Tapper the visitor's answer has one line per answer, each with its own copy button:
window.tapper.consent("GRANTED");
window.tapper.consent("DENIED");
Hand them to whoever manages your consent banner:
- Call the line that matches the visitor's answer on every page load, as soon as the answer is known.
- Call it again whenever the visitor changes their answer.
- Only pass the visitor's actual choice, never a default you configured.
Your monitoring and conversion scripts stay as they are.
How you classify Tapper under your privacy rules, and which consent you collect, are your decisions. What the script stores in each case is in Consent and Cookies on docs.tapper.ai.
Related
Was this helpful?
Still need help?
Chat with our team and mention this article.