

Allow Tapper in your Content Security Policy
If the monitoring script is installed, even firing in Google Tag Manager, but Tapper shows no visits or a high failed script load rate, your site's Content Security Policy (CSP) may be blocking it.
Why it happens
A CSP tells the browser where scripts, images and connections may come from, and refuses anything else. If Tapper's hosts are not on it, every browser refuses the monitoring script. The tag still fires in Google Tag Manager, but Tapper never receives the visit.
Confirm it is the policy
- Open your website in Chrome.
- Open DevTools (right-click the page and choose Inspect).
- On the Console tab, look for "Refused to load the script" naming
https://monitor.tapper.ai/bundle.jsand saying it "violates the following Content Security Policy directive". If the policy refuses the script's inline code, the message starts "Refused to execute inline script". - On the Network tab, filter on
tapperand reload. A blockedbundle.jsrequest frommonitor.tapper.aipoints to the policy.
If you see either, change your policy, not the Tapper install.
Fix it
The sources are in Setup > Website > Monitoring, on the Install script and consent tab, in the Content Security Policy box under the monitoring script. Its copy button gives your developer the exact list.
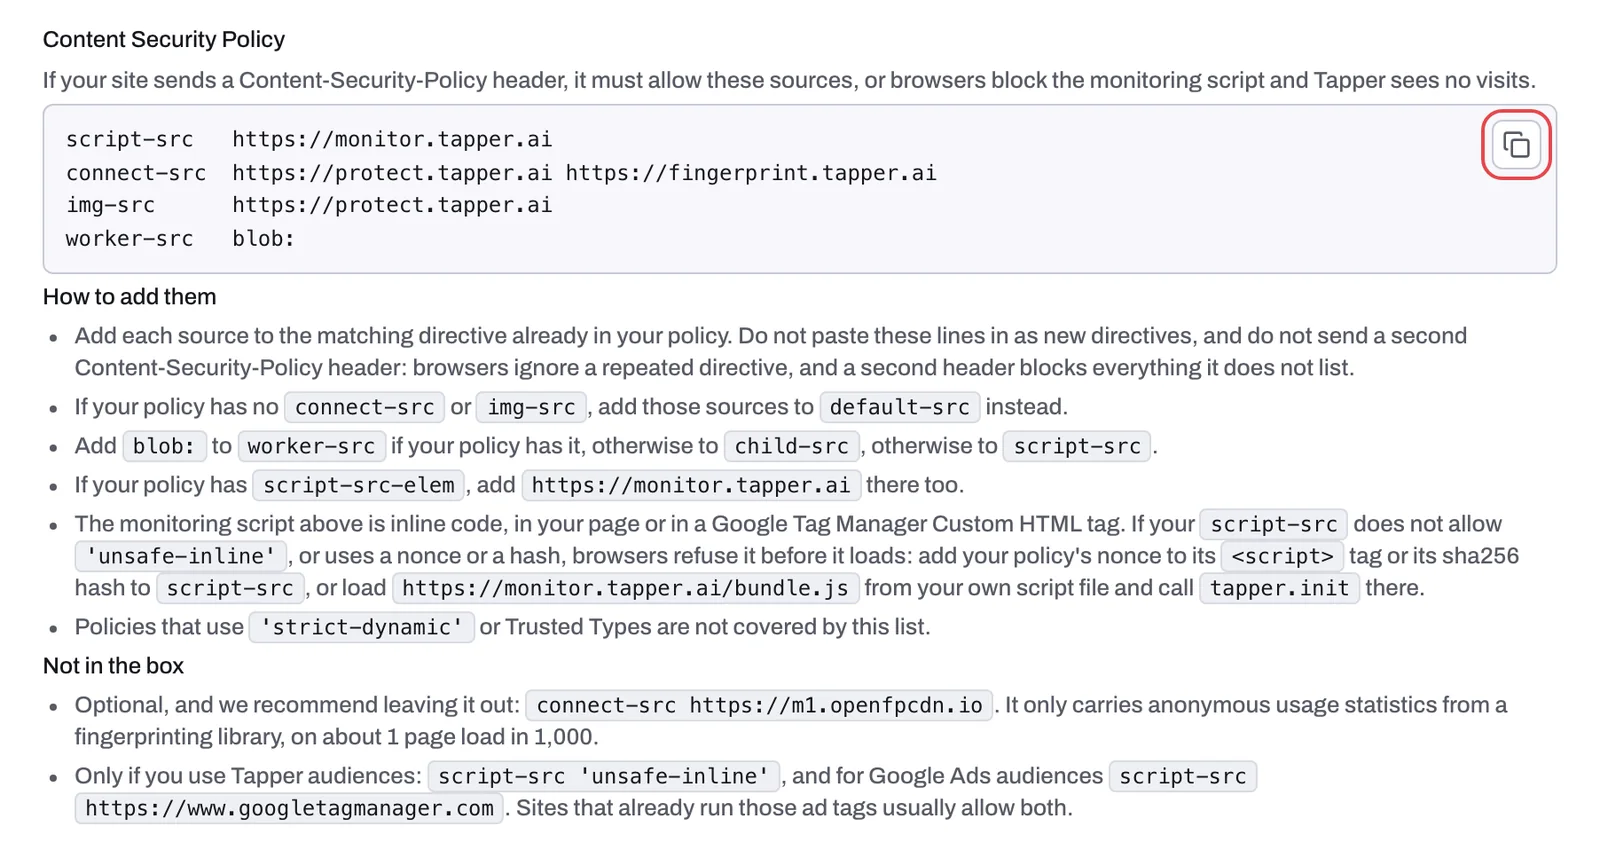
Every site with a policy needs these, one directive per line:
script-src   https://monitor.tapper.ai
connect-src  https://protect.tapper.ai https://fingerprint.tapper.ai
img-src      https://protect.tapper.ai
worker-src   blob:
Merge them into your existing policy:
- Add each source to the matching directive you already have. Do not add new directives or a second Content-Security-Policy header: browsers ignore a repeated directive, and a second header blocks everything it does not list.
- No
connect-srcorimg-src? Add those sources todefault-src. - Add
blob:toworker-srcif your policy has it, otherwise tochild-src, otherwise toscript-src. - If you have
script-src-elem, addhttps://monitor.tapper.aithere too. - The monitoring script is inline code, in your page or a Google Tag Manager Custom HTML tag. If your
script-srclacks'unsafe-inline', or uses a nonce or hash, browsers refuse it. Add your nonce to its<script>tag or its sha256 hash toscript-src, or loadhttps://monitor.tapper.ai/bundle.jsfrom your own script file and calltapper.initthere. - Policies using
'strict-dynamic'or Trusted Types are not covered by this list.
Not in the box
connect-src https://m1.openfpcdn.iois optional, and the app recommends leaving it out.- Only if you use Tapper audiences:
script-src 'unsafe-inline', plusscript-src https://www.googletagmanager.comfor Google Ads audiences. Sites that run those ad tags usually allow both.
If it still happens
- Reload your site and check the Console again. A new "Refused to" message names the directive that still needs a source.
- Then check that the monitoring script is working.
- Not sure where your policy is set? Forward this article to your developer or security team, or write to support@tapper.ai.
Related
Was this helpful?
Still need help?
Chat with our team and mention this article.