

Configure your identity provider for Tapper SSO
On this page
Create an application for Tapper in your identity provider, then bring three values back to Tapper. The steps are the same in Okta, Microsoft Entra, Auth0 and Ping. The Tapper side is in Set up single sign-on (SSO) for your workspace.
Before you start
- You need admin rights in your identity provider.
- Tapper uses OpenID Connect only. Do not create a SAML application.
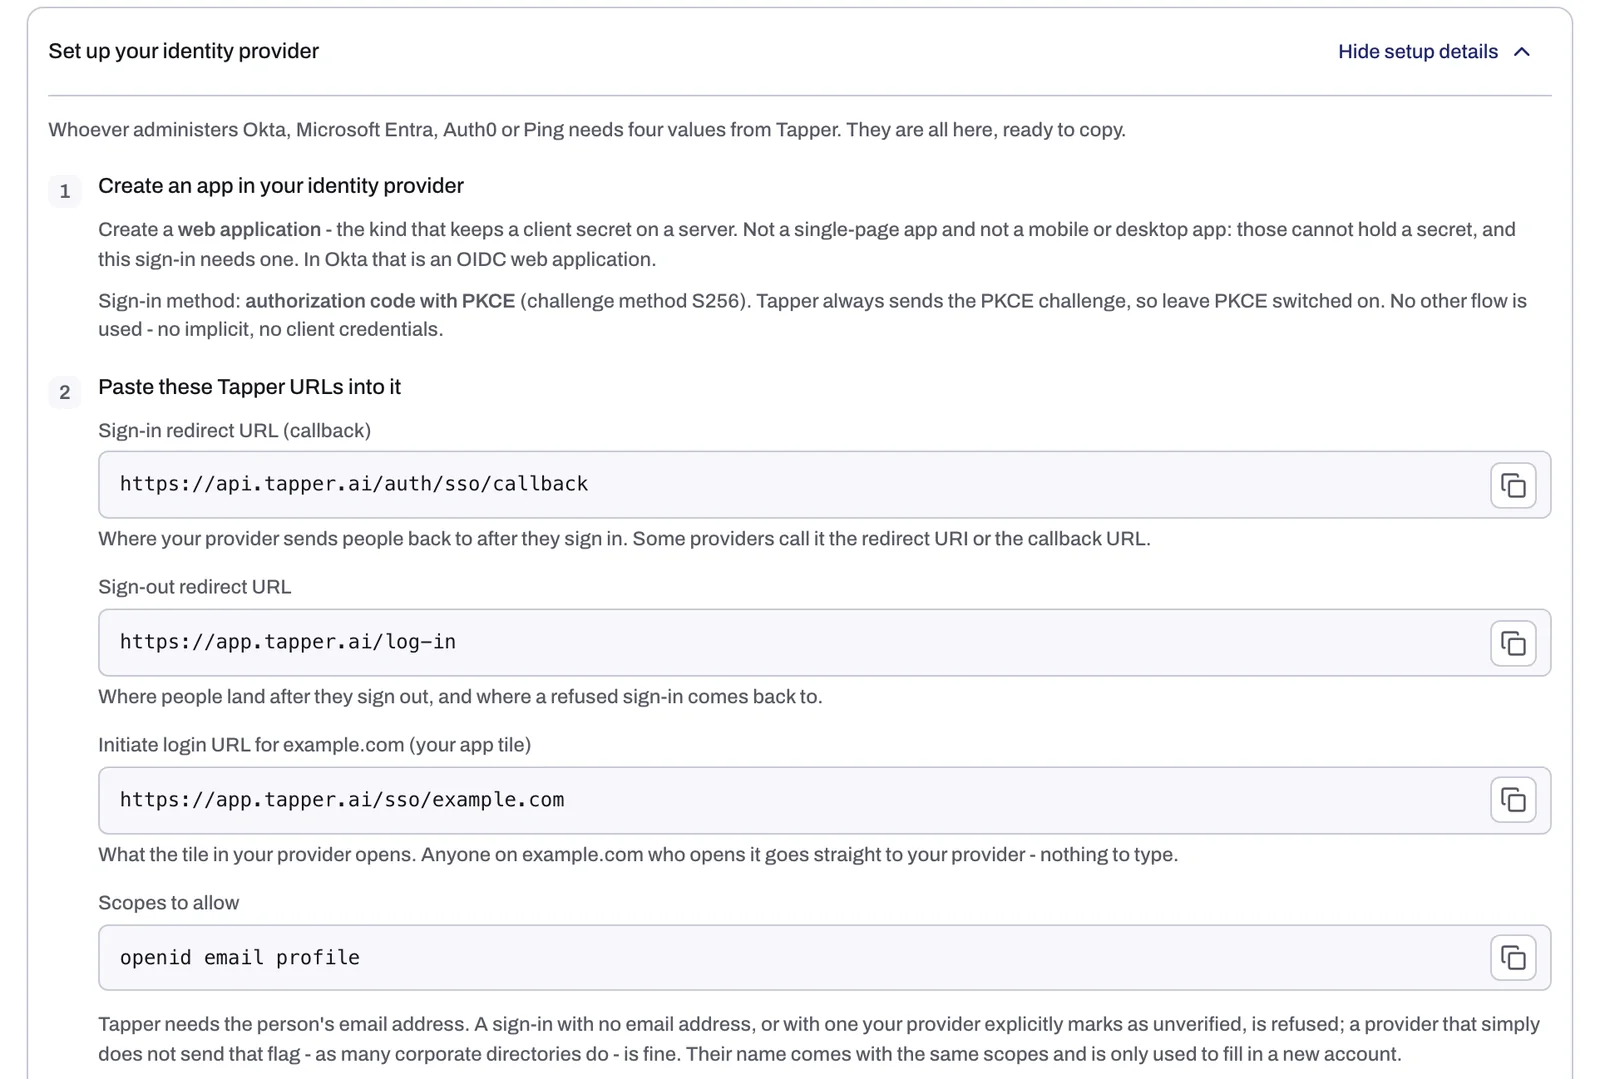
- An Owner or Admin can copy every value below from Settings, Single sign-on, in the Set up your identity provider panel (click its title if it is closed).
Values to paste into your provider
| Setting in your provider | Value |
|---|---|
| Sign-in redirect URL (callback, often called redirect URI) | https://api.tapper.ai/auth/sso/callback |
| Sign-out redirect URL | https://app.tapper.ai/log-in |
| Initiate login URL (the Tapper tile in your app launcher) | https://app.tapper.ai/sso/yourcompany.com, with your own domain |
| Scopes | openid email profile |
| Sign-in flow | Authorization code with PKCE, challenge method S256 |
Tapper needs each person's email address. A sign-in with no email address, or one your provider marks as unverified, is refused. A provider that does not send that flag at all is fine.
Create the application
- Create a new OpenID Connect web application, the kind that keeps a client secret on a server (in Okta, an OIDC web application). A single-page, mobile or desktop app cannot hold the client secret.
- Set the flow to authorization code with PKCE (
S256) and leave PKCE on. - Paste the callback and sign-out redirect URLs.
- Allow the scopes
openid email profile. - For a Tapper tile in your app launcher, paste the initiate login URL with your own domain.
- Give the people or groups who will use Tapper access to the application.
Bring three values back to Tapper
Paste these into Settings, Single sign-on:
| In your provider | In Tapper |
|---|---|
| Issuer | Issuer URL |
| Client ID | Client ID |
| Client secret | Client secret |
Then add and verify your email domains: see Set up single sign-on (SSO) for your workspace.
Finding the issuer
The public guide Set Up Your Identity Provider shows, for Okta, Auth0, Microsoft Entra and Ping, the application type, grant type, scopes and claims, and where each shows its issuer.
In Okta, the issuer is your organization's own address, such as https://your-company.okta.com, with nothing after the host. A custom authorization server (one ending in /oauth2/default) refuses the sign-in unless its access policy includes the Tapper app, and your people see "You are not allowed to access this app".
About the app tile
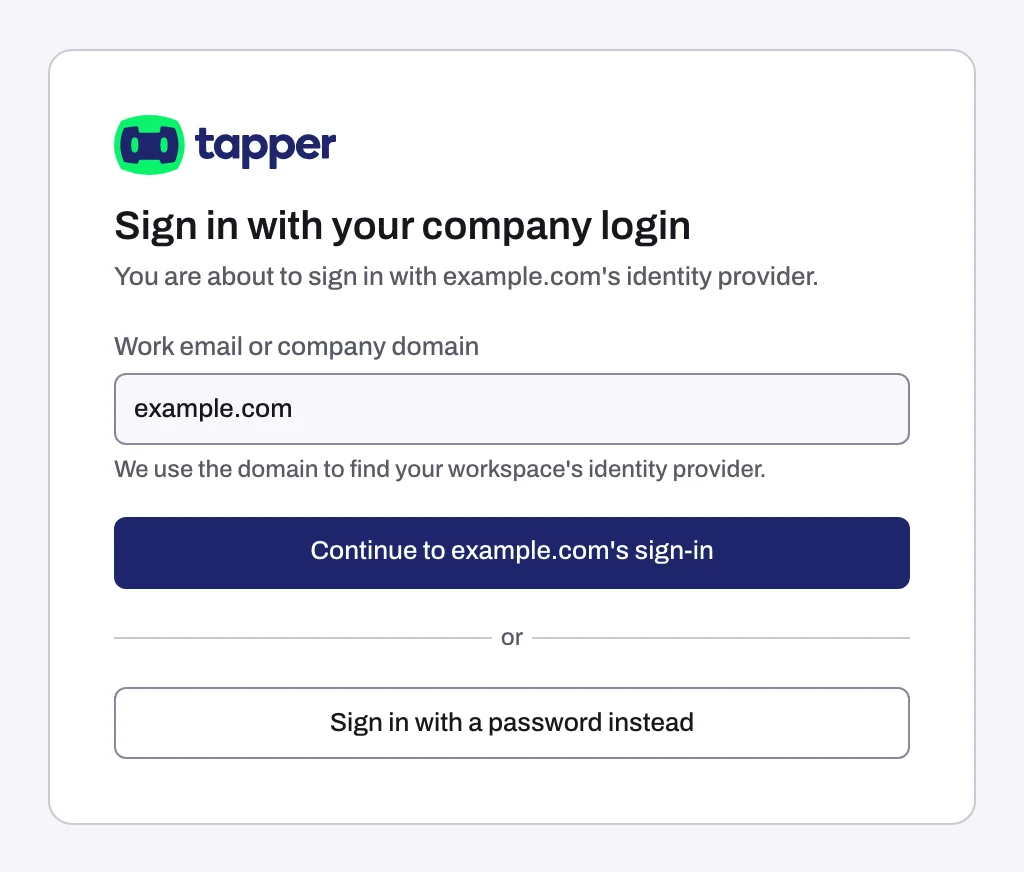
Use the initiate login URL with a domain you have verified in Tapper. Before that, use https://app.tapper.ai/sso, which asks for a Work email or company domain first.
The tile opens Log in with single sign-on with a Continue to yourcompany.com's login button. Tapper never starts the login by itself, so the person clicks that button.
Check it
In Tapper, click Test connection on the Single sign-on page to check the issuer before anyone signs in. If it fails, compare the issuer with the public guide.
Related
Was this helpful?
Still need help?
Chat with our team and mention this article.